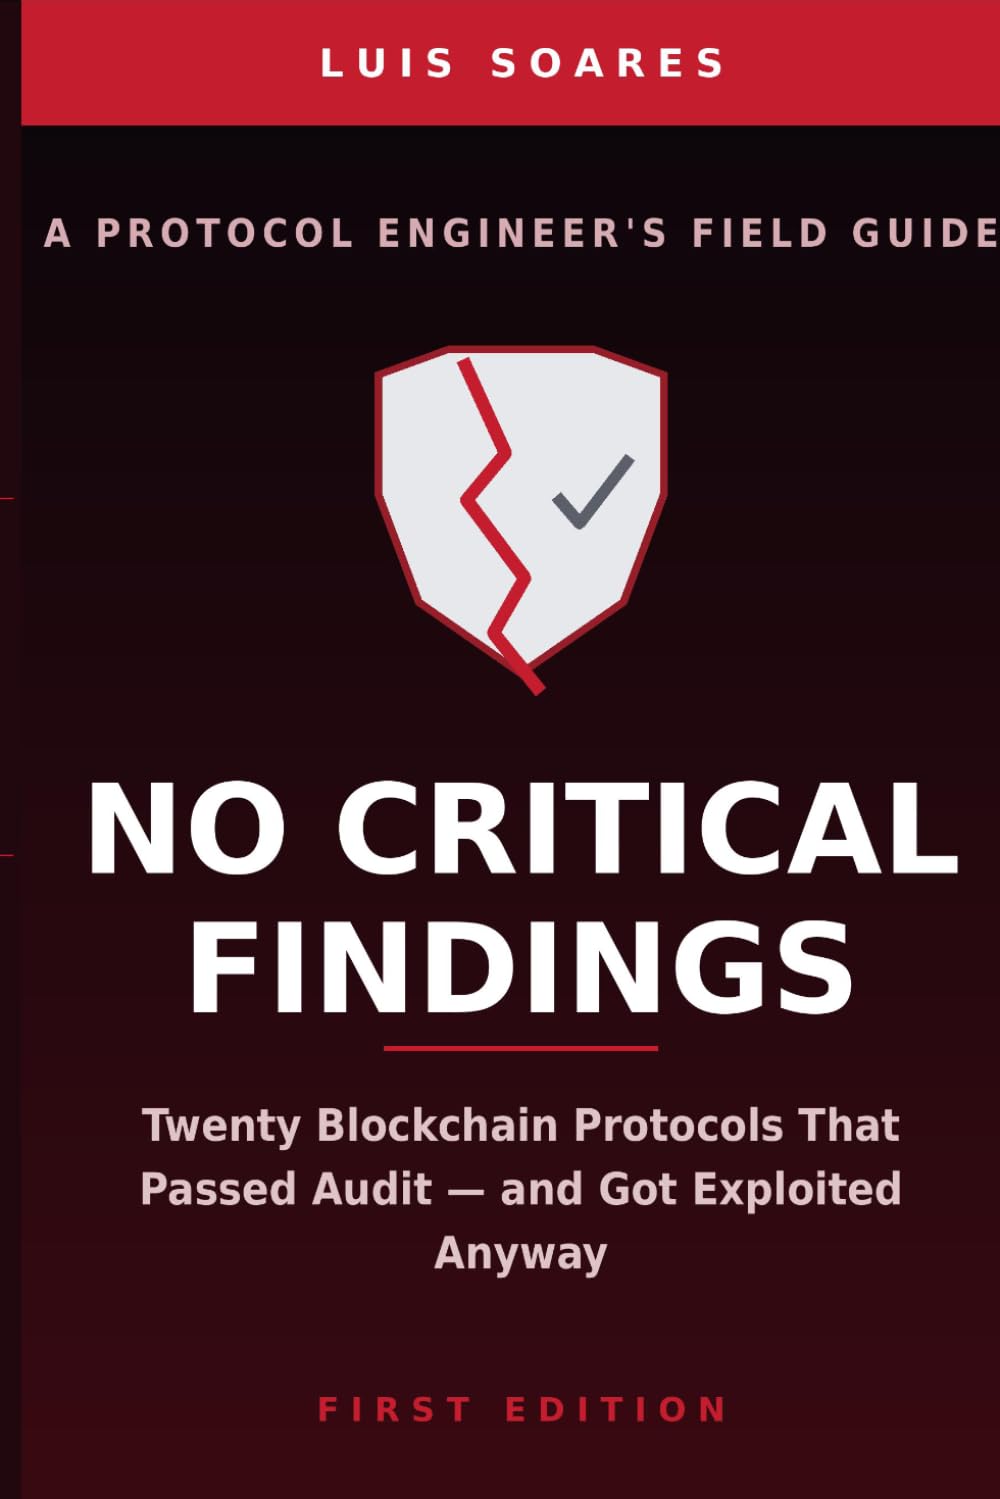
ler totalmente No Critical Findings: Twenty Blockchain Protocols That Passed Audit — and Got Exploited Anyway
por Luis Soares
No Critical Findings: Twenty Blockchain Protocols That Passed Audit — and Got Exploited Anyway
You've read an audit report that said "no critical or high findings." Weeks or months later, the protocol lost eight or nine figures anyway — not because the auditors were careless, and not because the team ignored their advice, but because the thing that broke was never a question the audit was built to answer. This book is twenty real incidents in that gap. Every protocol in these pages was reviewed — often by more than one respected firm, often more than once. Every one was exploited anyway, for reasons a source-code review was never positioned to catch: a price a flash loan could move within one transaction, a security property that held for every function except the one added six months after the audit closed, a compiler that quietly failed to preserve what the source code correctly specified, a governance vote that handed total control to whoever could borrow the most for twelve seconds, a validator set that turned out not to be as independent as its name implied. Inside, you'll find full technical breakdowns of incidents including: Each chapter follows the same rigorous structure: what the protocol did and why it looked clean, the vulnerable mechanism with real or faithfully reconstructed code, a working proof-of-concept you can actually run (Foundry for EVM chains, Anchor for Solana), the precise assumption that broke, an honest account of why the audit missed it, and a generalizable heuristic you can carry into your own review process. This book deliberately resists hindsight bias. It doesn't ask "how did nobody see this coming" — it reconstructs what a competent, honest reviewer actually knew at the time, so you can recognize the next boundary before it costs anyone nine figures. Written for experienced web3 developers, protocol architects, and security auditors who already know what gas, a PDA, and a reentrancy guard are, and who want a sharper, evidence-based account of exactly where "passed audit" and "safe" diverge — not a beginner's introduction to smart contract security.
Procurando No Critical Findings: Twenty Blockchain Protocols That Passed Audit — and Got Exploited Anyway? Aqui você encontra tudo sobre este livro de Luis Soares em 18 de setembro de 2026. Nesta página estão a descrição da obra, os detalhes da edição (163 páginas) e os formatos disponíveis para baixar: pdf, epub, txt, djvu. Se você gosta de Livros Internacionais, Computação, Informática e Mídias Digitais, Programação, Algoritmos, explore também outros títulos da mesma categoria no Encontrando os melhores livros. Veja ainda as outras obras de Luis Soares em nosso catálogo.
Autores populares
Icon Group International (283) Publishing lmgdaw (250) Nikolay Krechet (145) Kennie B Journals (120) Charles Nehme (106) Riddler Books (105) webmarbook design (104) Mint and Cherry Notebooks (82) Jillo Trukudo (80) Ondrej Sarek (76) Iwona Makara (74) Just Visualize It (72) Moonpeak Library (69) Quick Witted Coconut (69) Mary Hirose (67) Talor Press (67) Various (67) Marina Buchholz B.Eng (58) Miller Sye (58) NAK Legal Publishing (58)Principais publicadores
Independently published Forgotten Books Routledge Taschen Dover Publications Wiley Oxford University Press CRC Press Kessinger Publishing Princeton University Press Cambridge University Press Springer Bloomsbury Academic O'Reilly Media Hal Leonard Publishing Corporation Tuttle Publishing Rizzoli International Publications Content provided by MemoryLane.com Editorial Tirant lo Blanch Thames & Hudson