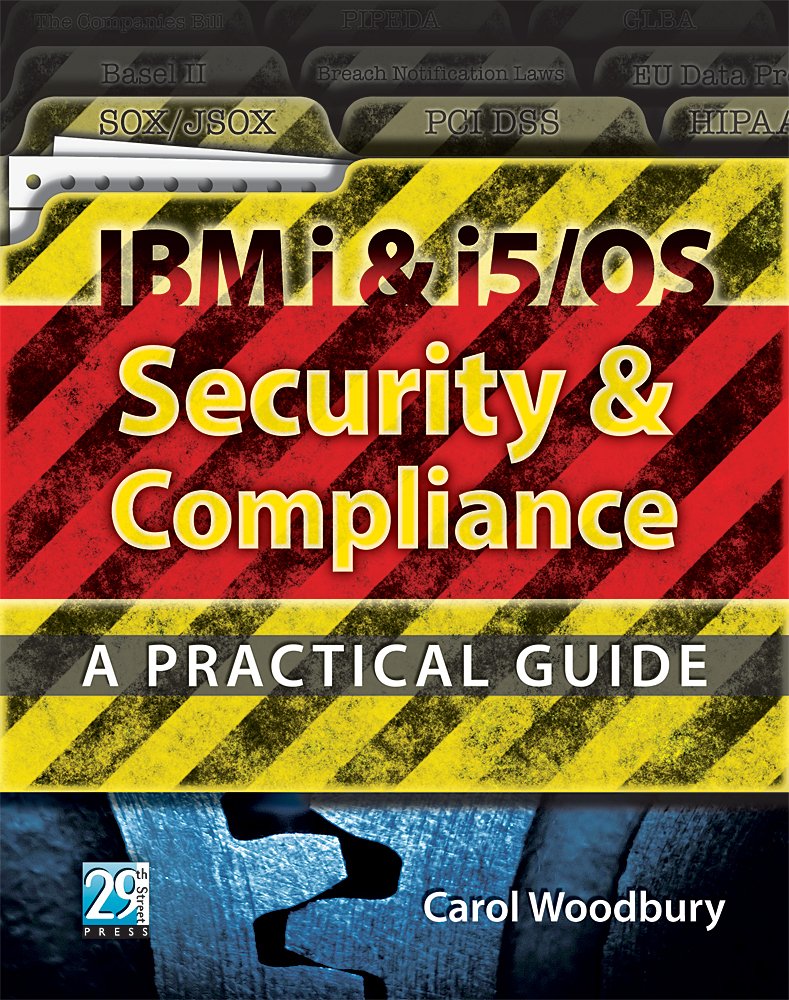
txt IBM I & I5/Os Security & Compliance: A Practical Guide
por Carol Woodbury
Descrição do livro
Get a fresh look at the world of IBM i and i5/OS security in this comprehensive book by one of the industrys leading authorities on security. Security consultant Carol Woodbury takes her extensive experience designing and implementing security on IBM systems and makes it relevant for todays world. Throughout the book, she discusses issues that organizations need to address for compliance requirements, providing best practices as well as alternatives and options for compensating controls when best practices cannot be applied.Building on the foundation laid by the popular Experts Guide to OS/400 & i5/OS Security, this edition features completely updated information throughout. New chapters address compliance requirements for IBM i, implementing role-based access (RBAC), implementing object-level security, and creating a security incident response plan. Carol Woodburys methodology for implementing object-level security is described in detail. Topics include determining a systems current settings, default access requirements, process access, and the rollout of new application security models. The book presents this information in a clear and informative way that lets even non-security professionals understand and apply the concepts.This book is a must-read for any auditor, system administrator, security officer, or compliance officer who works with IBM i or i5/OS.Contents Chapter 1: Security The Real Reason Youre Reading This Book Chapter 2: Policies and Procedures Chapter 3: Security at the System Level Chapter 4: The Facts About User Profiles Chapter 5: Service Tools Security Chapter 6: Object-Level Security Chapter 7: Security Considerations for the IFS Chapter 8: Securing Your Printed Output Chapter 9: Encryption Chapter 10: Connecting to the System Chapter 11: Internet Security Chapter 12: Evaluating Applications Current Implementations and Designing New Ones Chapter 13: Role-based Access (RBAC) Chapter 14: Role-based Access for IT Chapter 15: Auditing Chapter 16: Implementing Object-Level Security Chapter 17: Maintaining Compliance Chapter 18: Preparing for the Worst: Creating a Security Incident Response Plan Chapter 19: Creating a Security Awareness Program
Autores populares
Icon Group International (283) Publishing lmgdaw (250) Nikolay Krechet (145) Kennie B Journals (120) Charles Nehme (106) Riddler Books (105) webmarbook design (104) Mint and Cherry Notebooks (82) Jillo Trukudo (80) Ondrej Sarek (76) Iwona Makara (74) Just Visualize It (72) Moonpeak Library (69) Quick Witted Coconut (69) Mary Hirose (67) Talor Press (67) Various (67) Marina Buchholz B.Eng (58) Miller Sye (58) NAK Legal Publishing (58)