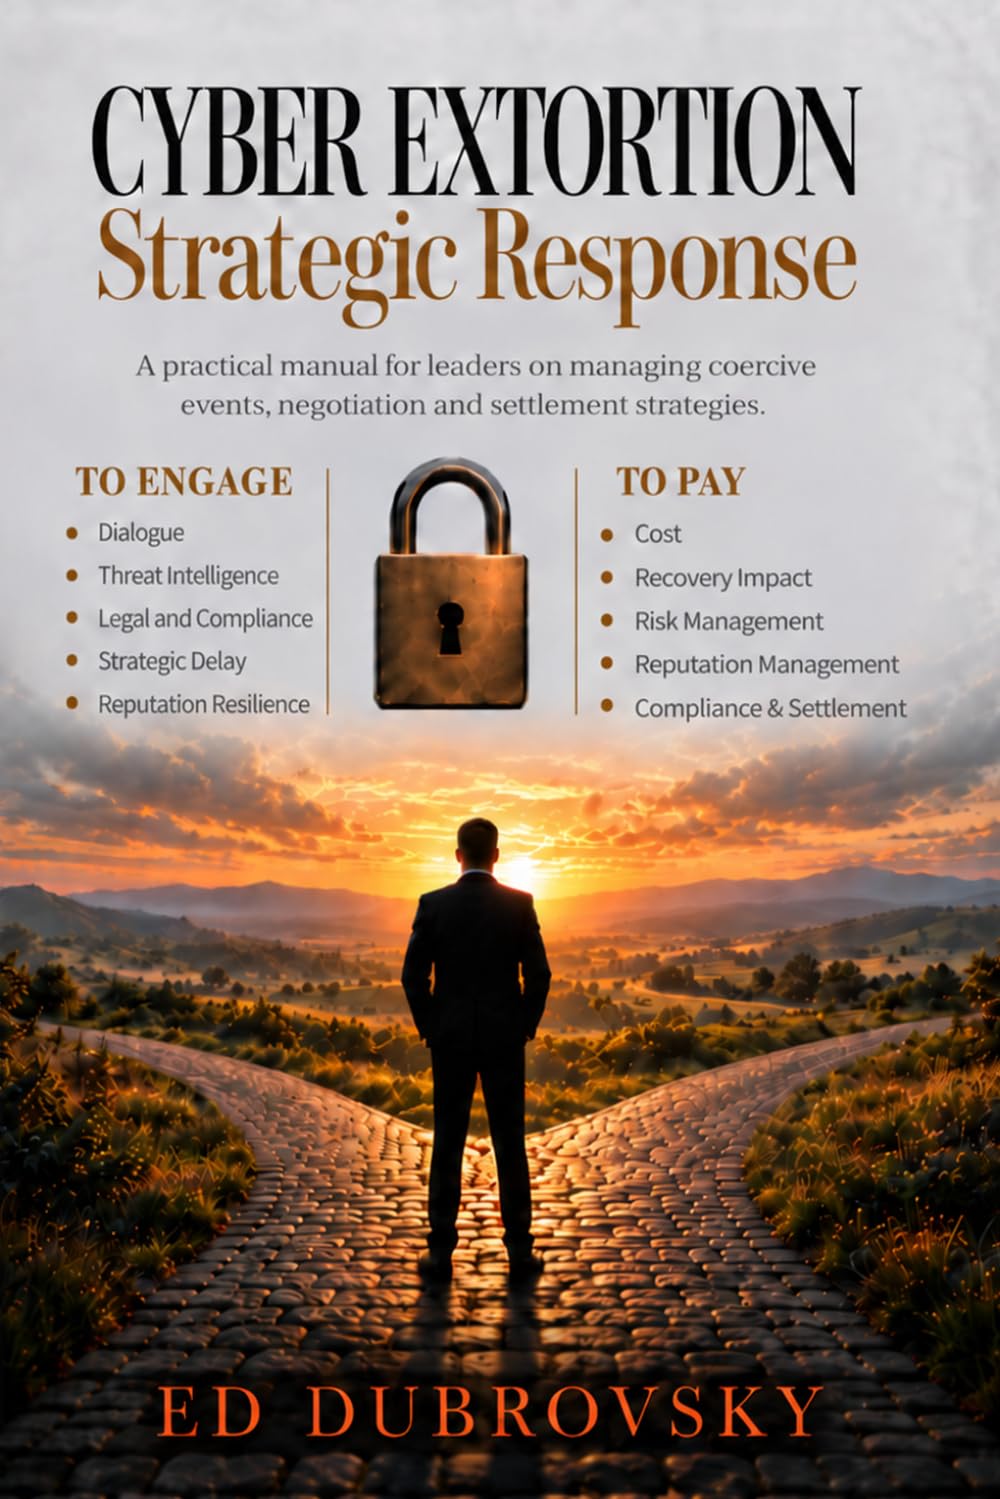
Descrição do livro
Ransomware is not just a technology problem. It is a leadership crisis. Your systems are down. Sensitive information may be in criminal hands. The deadline is approaching. Your advisors do not all agree and you own the decisions. What do you do next? CYBER EXTORTION: Strategic Response takes readers beyond the ransom note and into the decisions that determine how an organization responds, recovers, and protects what matters. Drawing on more than thirty years in cybersecurity and experience across thousands of matters, Ed Dubrovsky challenges the assumption that cyber extortion can be managed through a standard script, a predictable discount, or a simple "pay or do not pay" rule. He explains why effective response demands more than technical recovery: it requires intelligence, judgment, communication, and a strategy built around the organization's actual circumstances. At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move. Through practical frameworks and illustrative composite scenarios, Dubrovsky examines the people, pressures, and competing interests behind a cyber-extortion crisis. He explores how attackers think, how assumptions become dangerous, why language and translation can change a negotiation, and how leadership teams can avoid mistaking confidence for evidence. Readers will learn how to: - Separate facts, assumptions, and criminal claims, and identify the information that could change a decision. - Evaluate whether to engage, whether to negotiate, and whether payment could serve a defined business objective, without confusing those decisions. - Apply negotiation tools such as anchoring, strategic silence, framing, proof requests, and controlled concessions within a broader response strategy. - Weigh recovery options, business interruption, reputational exposure, legal and sanctions considerations, insurance requirements, and the consequences of both payment and refusal. - Establish decision authority, coordinate advisers, document the rationale for difficult choices, and recognize when new evidence requires a change of course. This is not a collection of messages to copy into a criminal's chat window. Nor is it an argument that every organization should pay, or that refusal is always the right answer. It is a practical manual for understanding the options, testing the advice, and making deliberate decisions when every available course carries risk. Written for executives, board members, business owners, legal counsel, cybersecurity leaders, insurers, and incident-response professionals, the book combines strategic perspective with a negotiator's toolkit, executive checklists, and a structured decision record. It is designed to support preparation before an incident and clearer thinking during one. Success is not simply a lower ransom demand. It is an outcome measured against the organization's survival, recovery, responsibilities, and future. The criminal may set the demand. Your organization must set the strategy.
Autores populares
Icon Group International (283) Publishing lmgdaw (250) Nikolay Krechet (145) Kennie B Journals (120) Charles Nehme (106) Riddler Books (105) webmarbook design (103) Mint and Cherry Notebooks (82) Jillo Trukudo (80) Ondrej Sarek (76) Iwona Makara (74) Just Visualize It (71) Moonpeak Library (69) Quick Witted Coconut (69) Various (68) Mary Hirose (67) Talor Press (67) Marina Buchholz B.Eng (58) Miller Sye (58) NAK Legal Publishing (58)