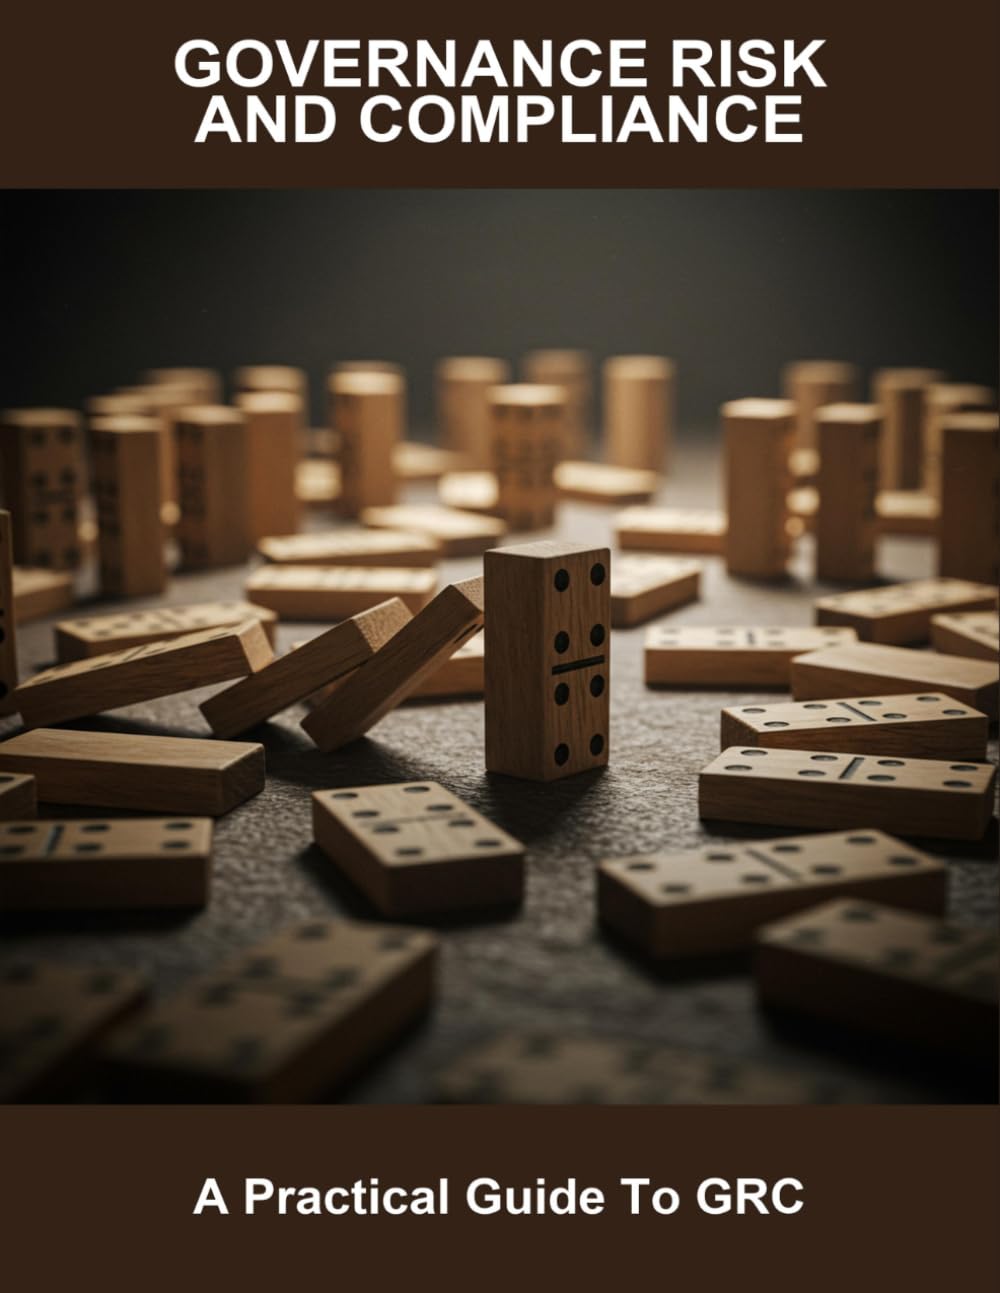
txt Governance Risk And Compliance: A Practical Guide To Grc
por Takashi Sakurai
Descrição do livro
The modern enterprise operates in a constant state of unprecedented flux, where the notion of a stable business environment is a dangerous fantasy. Rapid globalization, an accelerating torrent of technological advancements, and a regulatory environment shifting with dizzying speed conspire to create a landscape fraught with complexity and unseen dangers. For leaders grappling with multi-continental supply chains, evolving data privacy laws, sophisticated cybersecurity threats, and relentless ESG demands, traditional, fragmented approaches to oversight are no longer merely inefficient—they're a direct path to disaster. *Governance Risk And Compliance: A Practical Guide To Grc* offers the essential framework to navigate this volatility, transforming overwhelming challenges into strategic opportunities.
Many organizations still cling to outdated, siloed methods, treating Governance, Risk Management, and Compliance as distinct functions. Legal handles compliance, IT manages cybersecurity, finance manages controls, and audit checks boxes, each operating independently. This disconnect isn’t just wasteful; it generates dangerous blind spots. Consider the multi-million-euro penalties leveled against tech giants for data processing failures, or the liabilities arising when a new product launches without adequate regulatory input. This fragmented approach creates an expensive, redundant cycle that drains resources, stifles innovation, and actively hinders the reliable achievement of strategic objectives. Without a unified view, organizations remain vulnerable to crippling fines, mandatory recalls, and devastating reputational harm, unable to build the principled performance required for sustained success.
This guide introduces integrated GRC not as another layer of bureaucracy, but as the essential “unseen architecture of success.” Moving “beyond the checklist,” it deconstructs Governance, Risk Management, and Compliance, bringing these disparate functions together into a coherent, unified system. You’ll discover how to build a robust framework that provides a single, comprehensive view of your organization's risks, controls, and compliance obligations. This integrated approach enables cross-functional awareness, coordinated strategic responses, and proactive decision-making. By weaving GRC directly into your enterprise capabilities, you can confidently address uncertainty and act with integrity, ensuring your strategic initiatives are not just ambitious, but reliably achievable.
With *Governance Risk And Compliance*, you will gain the clarity and tools to:
* Achieve your strategic objectives reliably, even amidst rapid market shifts and evolving threats.
* Build a resilient, adaptable organization capable of responding proactively to new regulations and emerging technologies.
* Optimize resource allocation by eliminating redundant efforts and fostering cross-departmental collaboration.
* Gain a significant competitive edge by making informed decisions that balance innovation with risk and compliance.
* Protect your organization from costly fines, reputational damage, and operational disruptions stemming from non-compliance.
* Foster a culture of integrity, accountability, and ethical decision-making across all levels of your enterprise.
Stop managing complexity—start mastering it. This practical guide provides the insights and actionable strategies to transform your GRC landscape, turning potential liabilities into powerful drivers of “Principled Performance” and lasting success.
Autores populares
Icon Group International (283) Publishing lmgdaw (250) Nikolay Krechet (192) Kennie B Journals (120) Charles Nehme (106) Riddler Books (105) webmarbook design (103) Vários Autores (87) Unknown Author (85) Mint and Cherry Notebooks (82) Jillo Trukudo (80) Various (79) Evgeniia Naumchenko (78) Ondrej Sarek (76) NAK Legal Publishing (75) Iwona Makara (74) Just Visualize It (71) Moonpeak Library (69) Quick Witted Coconut (69) Mary Hirose (67)